CIS Controls for Threat Mitigation
Explore how CIS Safeguards map to MITRE ATT&CK techniques to assess defensive coverage, identify gaps, and support threat-informed security control implementation.
Explore how CIS Safeguards map to MITRE ATT&CK techniques to assess defensive coverage, identify gaps, and support threat-informed security control implementation.
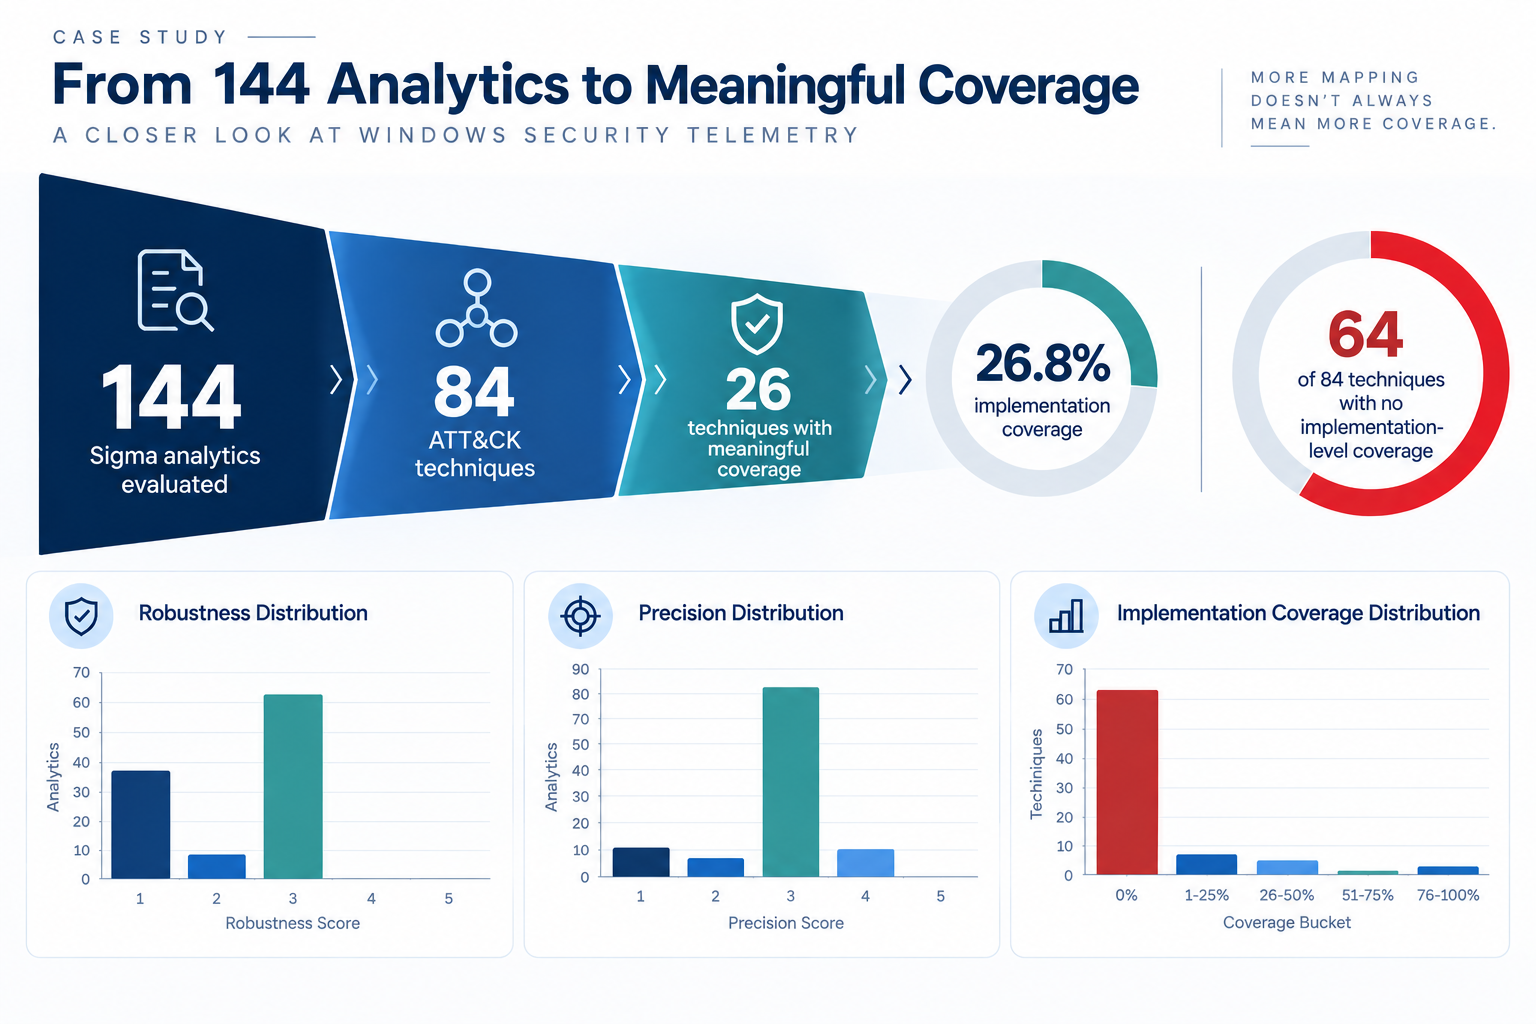
A case study of 144 Sigma analytics using Windows Security log sources shows why ATT&CK mappings alone do not reveal the depth or quality of detection coverage.
Summiting the Pyramid introduces implementation coverage and detection quality to help defenders measure the depth and effectiveness of detection coverage beyond an ATT&CK heatmap.
Attack Flow v4 helps defenders turn incident evidence into connected flows, add the context needed for action, and communicate decisions across technical and executive audiences.
Secure AI expanded MITRE ATLAS™ with new techniques, mitigations, case studies, a Technique Maturity filter, and rapid-response and emulation capabilities to strengthen defense of AI-enabled systems.

MITRE Fight Fraud Framework (F3) is a behavior-based model of fraud actor tactics and techniques that gives fraud and cyber defenders a shared structure to describe incidents, relate events, and disrupt fraud outcomes.
MITRE CTID’s latest ambiguous techniques research turns context into confidence with minimum telemetry requirements and a confidence scoring model that helps detection engineers pick the right log sources for robust, low-noise detections.
Threat-informed defense changes the game on the adversary. Threat-informed defenders read their adversaries’ playbooks and then orchestrate a defense based on that knowledge. MITRE ATT&CK® is the core of threat-informed defense as our framework of adversary tactics, techniques, and procedures …
MITRE ATLAS™ analyzed OpenClaw incidents that showcase how AI-first ecosystems introduce new exploit execution paths. OpenClaw is unique because it can independently make decisions, take actions, and complete tasks without continuous human oversight. By mapping the patterns and behaviors to ATLAS …
Threats to cloud computing span multiple security domains, objectives, and layers of technology. Defenders must protect dynamic, shared environments while adversaries actively exploit misconfigurations, weak controls, and gaps between responsibility boundaries. To keep up, security cannot just focus …