CIS Controls for Threat Mitigations
CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
March 13, 2024
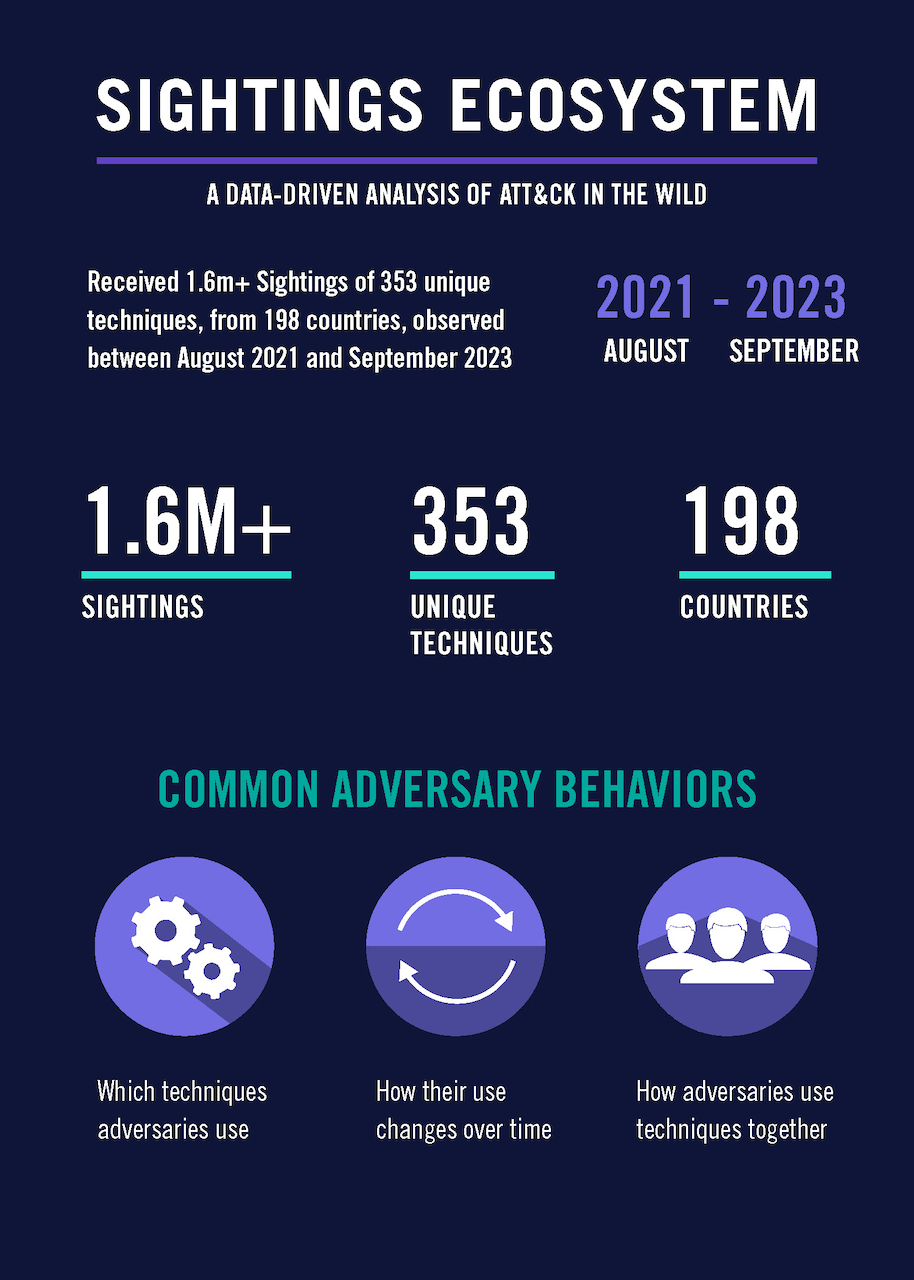
This project provides cybersecurity defenders and researchers with critical insight into real-world adversary behaviors mapped to ATT&CK. The ecosystem fundamentally advances the collective ability to see threat activity across organizational, platform, vendor, and geographical boundaries. Voluntarily contributed raw “sightings”, or observations of specific adversary TTPs, are anonymized, and aggregated to produce insights into the most commonly used attacker techniques.
Defenders lack visibility into which adversary behaviors they should focus their attention on first.
Build an ecosystem for organizations to safely contribute ATT&CK-specific detection data, empowering defenders to have clear insights what techniques attackers use in the wild.
The sightings ecosystem injects real-world data and insights from that data into the decision-making process of defenders, allowing them to focus their resources on the highest priority problems

CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
Summiting the Pyramid helps defenders measure the depth and quality of detection coverage beyond an ATT&CK heatmap. This release introduces …
Attack Flow helps defenders capture the entire scope of a cyber attack and communicate what matters. By representing actions, conditions, and …
Sign up for our "Stay Informed" mailing list to receive announcements for project publications, upcoming events, and other news about the Center.