CIS Controls for Threat Mitigations
CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
June 21, 2024
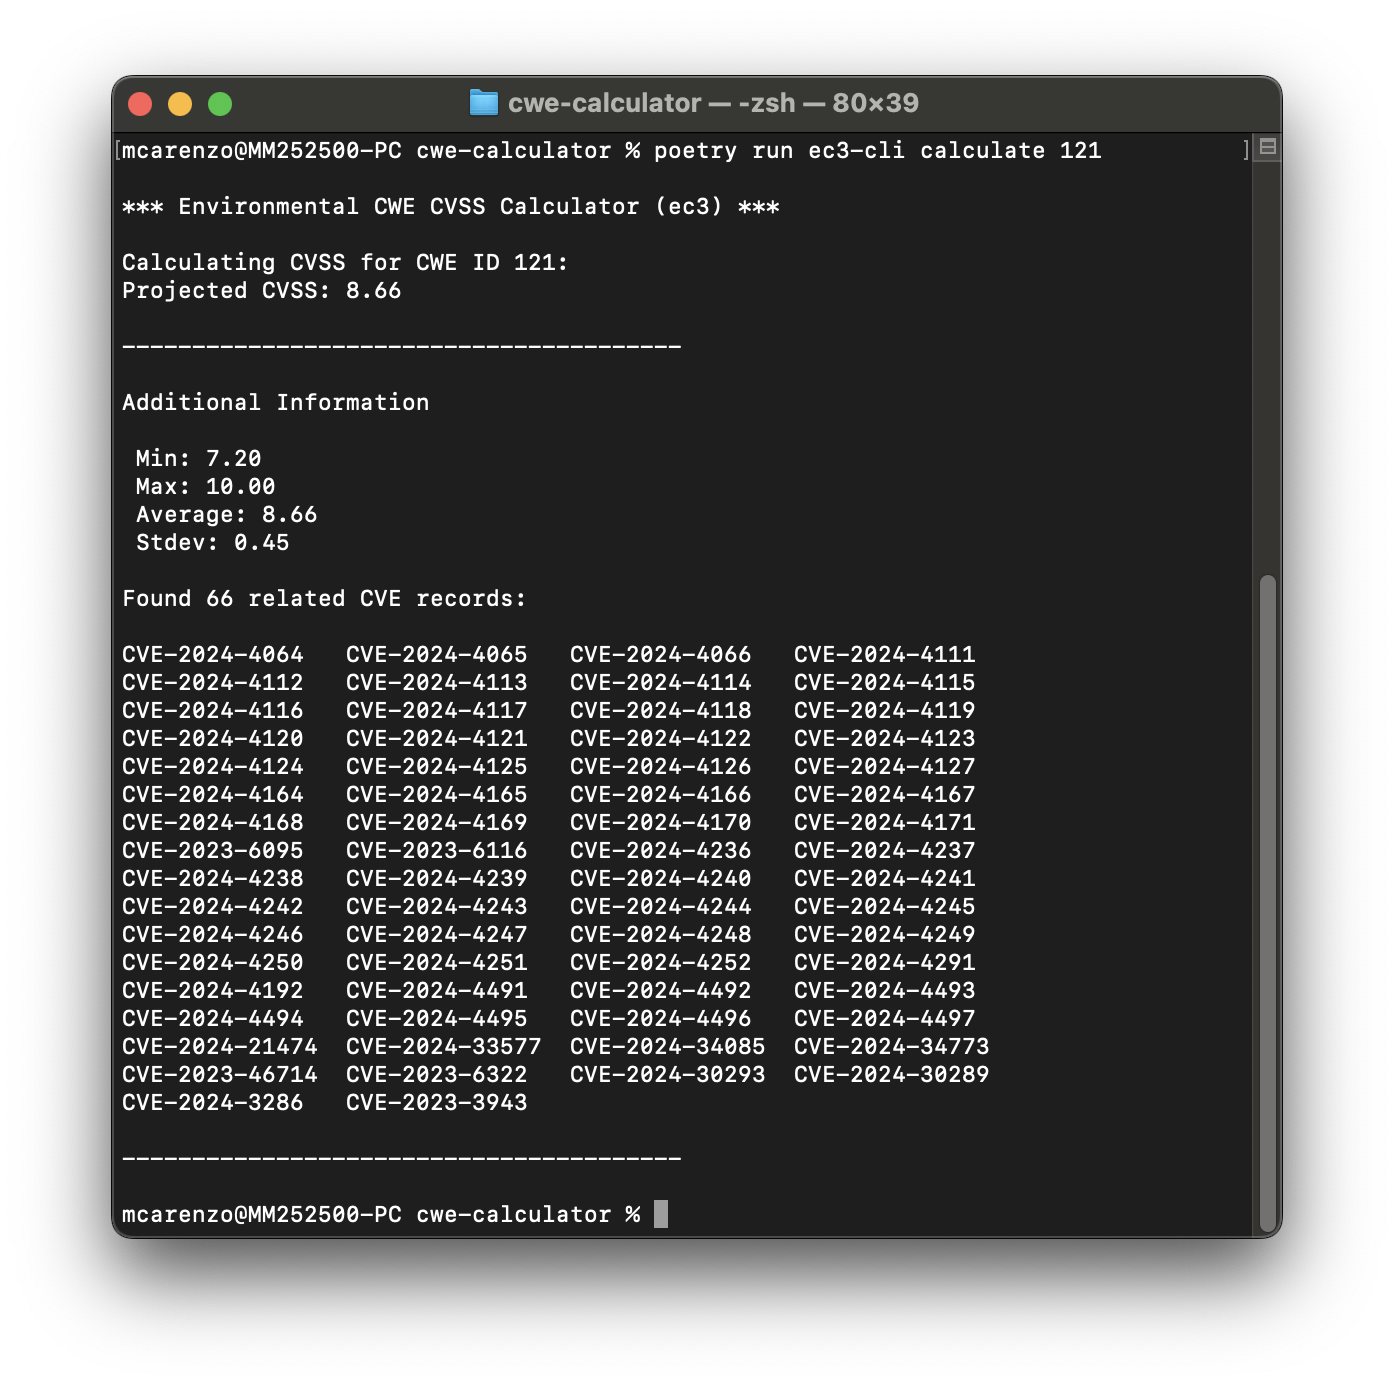
The software industry is faced with managing large numbers of software weaknesses (commonly identified by static-scanning tools using CWE ID reference), alongside large numbers of software vulnerabilities (CVEs), which all sit across many assets with differing security requirements. The calculator enables software development teams to score and prioritize discovered weaknesses empirically based on data in the National Vulnerability Database (NVD).
Without a common system of comparison across software weaknesses (CWEs) and software vulnerabilities (CVEs) that factors in environmental context, engineering teams cannot effectively prioritize their work, and thus waste cycles on wrong things while they miss opportunities to secure systems.
The CWE with Environmental CVSS Calculator will provide output that effectively enables a CWE in a specified environment to be priority ranked against a CVE in the same or different environment.
Software development teams will focus their limited resources on addressing the most dangerous issues.

CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
Summiting the Pyramid helps defenders measure the depth and quality of detection coverage beyond an ATT&CK heatmap. This release introduces …
Attack Flow helps defenders capture the entire scope of a cyber attack and communicate what matters. By representing actions, conditions, and …
Sign up for our "Stay Informed" mailing list to receive announcements for project publications, upcoming events, and other news about the Center.