CIS Controls for Threat Mitigations
CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
May 13, 2025
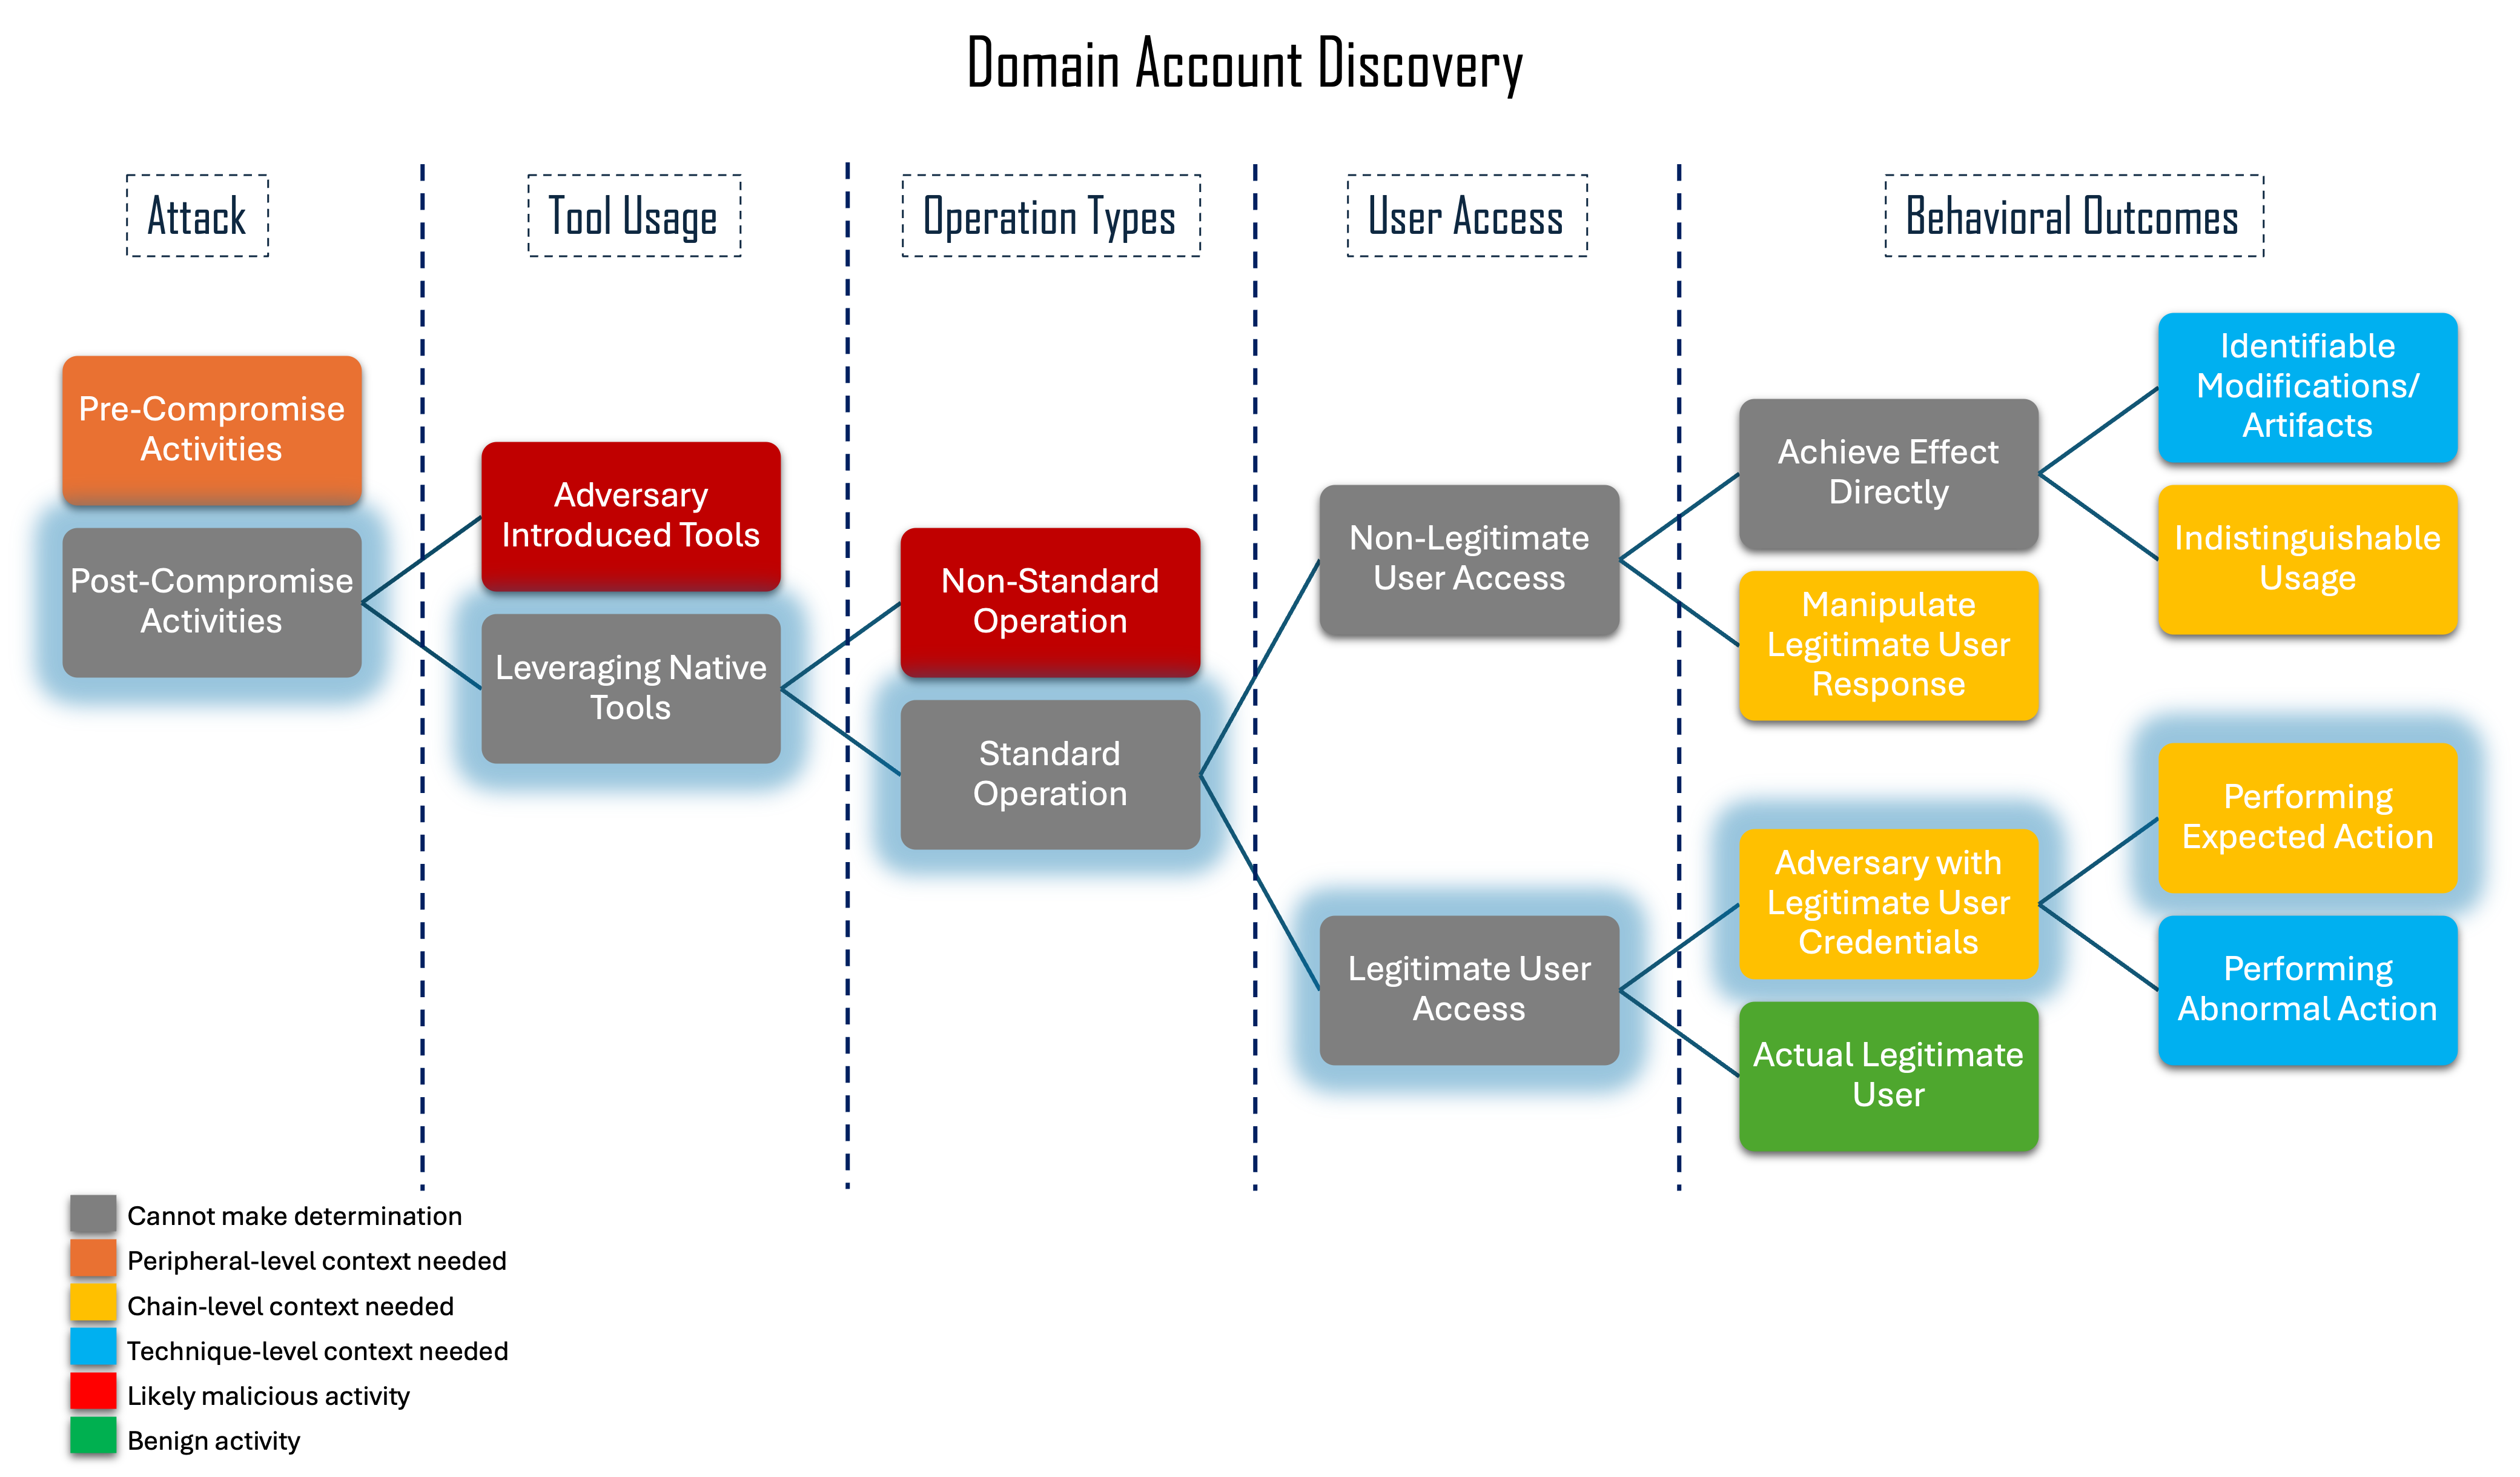
Building upon the research of Summiting the Pyramid, Ambiguous Techniques is a methodology to determine malicious intent behind seemingly benign behavior by applying contextual analysis to ATT&CK techniques. Reduce false positives and uncover adversarial use of living-off-the-land activity.
This is an old version of the Ambiguous Techniques project. For the latest version, see: Ambiguous Techniques.
Many ATT&CK techniques, especially those used in living-off-the-land activity, produce observables that are indistinguishable from benign behavior, making it difficult for defenders to determine malicious intent and resulting in unreliable or overly noisy detections.
Create a methodology that uses the surrounding context of a detection event to infer the intent of the actor, thus removing the ambiguity.
Reduce false positives and improve detection accuracy so defenders can prioritize the alerts that truly matter.

CIS Controls for Threat Mitigations connects the security capabilities of the Center for Internet Security’s Critical Security Controls to …
Summiting the Pyramid helps defenders measure the depth and quality of detection coverage beyond an ATT&CK heatmap. This release introduces …
Attack Flow helps defenders capture the entire scope of a cyber attack and communicate what matters. By representing actions, conditions, and …
Sign up for our "Stay Informed" mailing list to receive announcements for project publications, upcoming events, and other news about the Center.